
Permissions & roles
Overview
Legal practices require strict control over who can access information within a matter. At Smokeball, I worked on early design concepts for improving the platform’s permissions system to support more flexible and scalable access control.
The Problem
As firms grow, managing permissions across users becomes increasingly complex. Existing permission controls lacked the flexibility needed for larger teams and different organisational structures.
Firms needed better ways to define roles and manage access to different parts of the system.
My Role
Senior Product Designer responsible for exploring design concepts for a more structured permissions model.
This work involved collaborating with product and engineering teams to understand technical constraints and develop scalable design solutions.
Design Approach
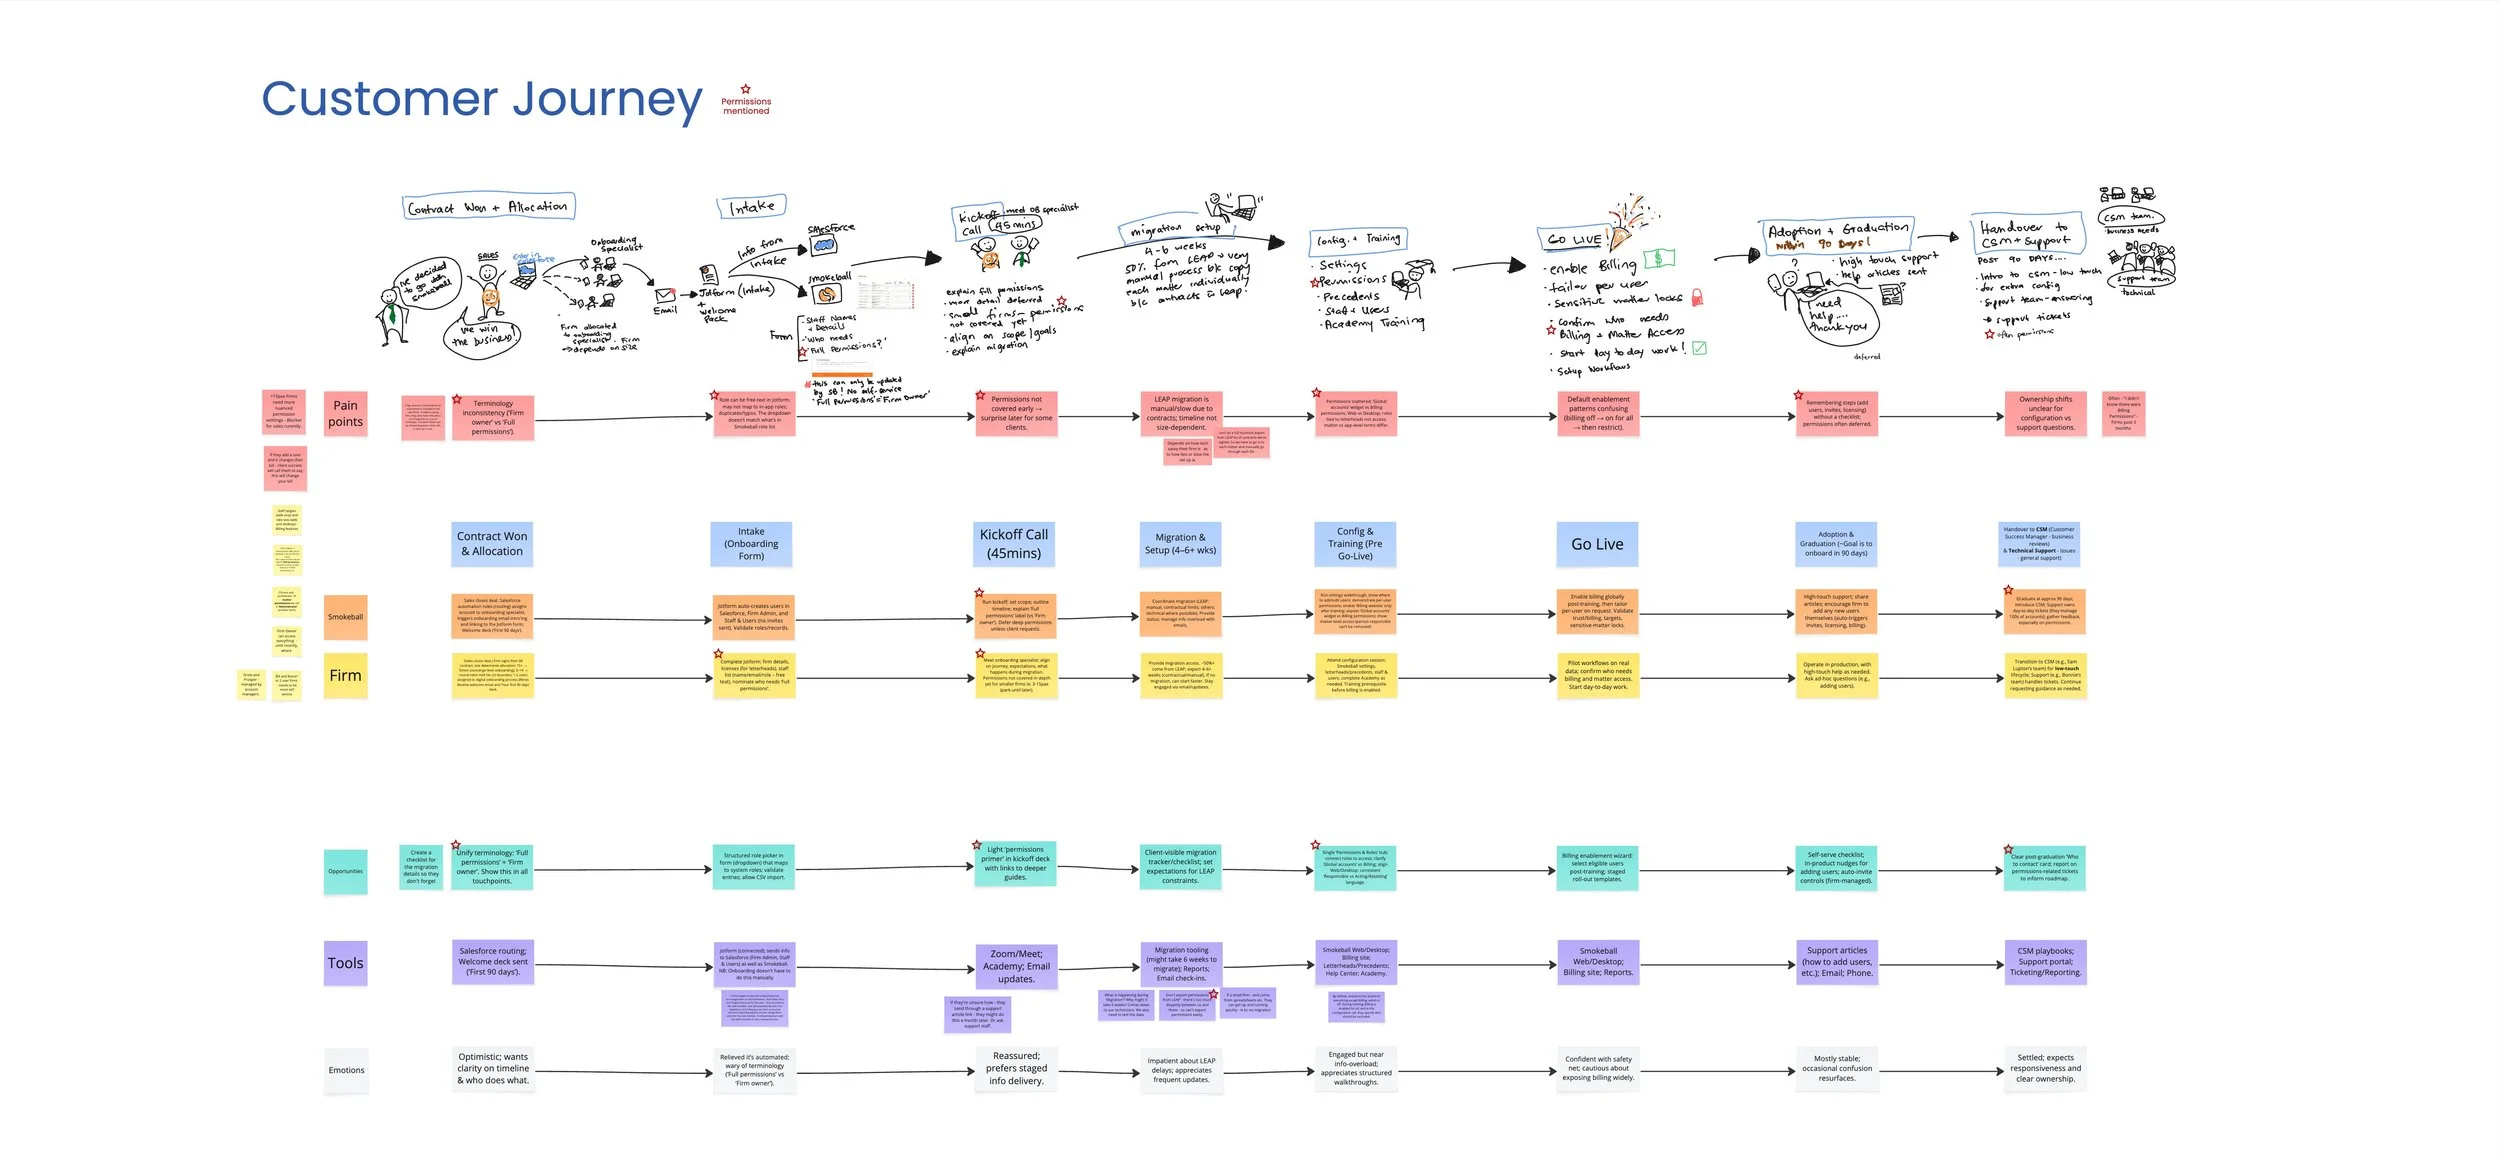
Mapping permission complexity
Legal practices often require different levels of access for partners, lawyers, support staff, and administrative roles.
I mapped common permission scenarios to understand how access should behave across the platform.
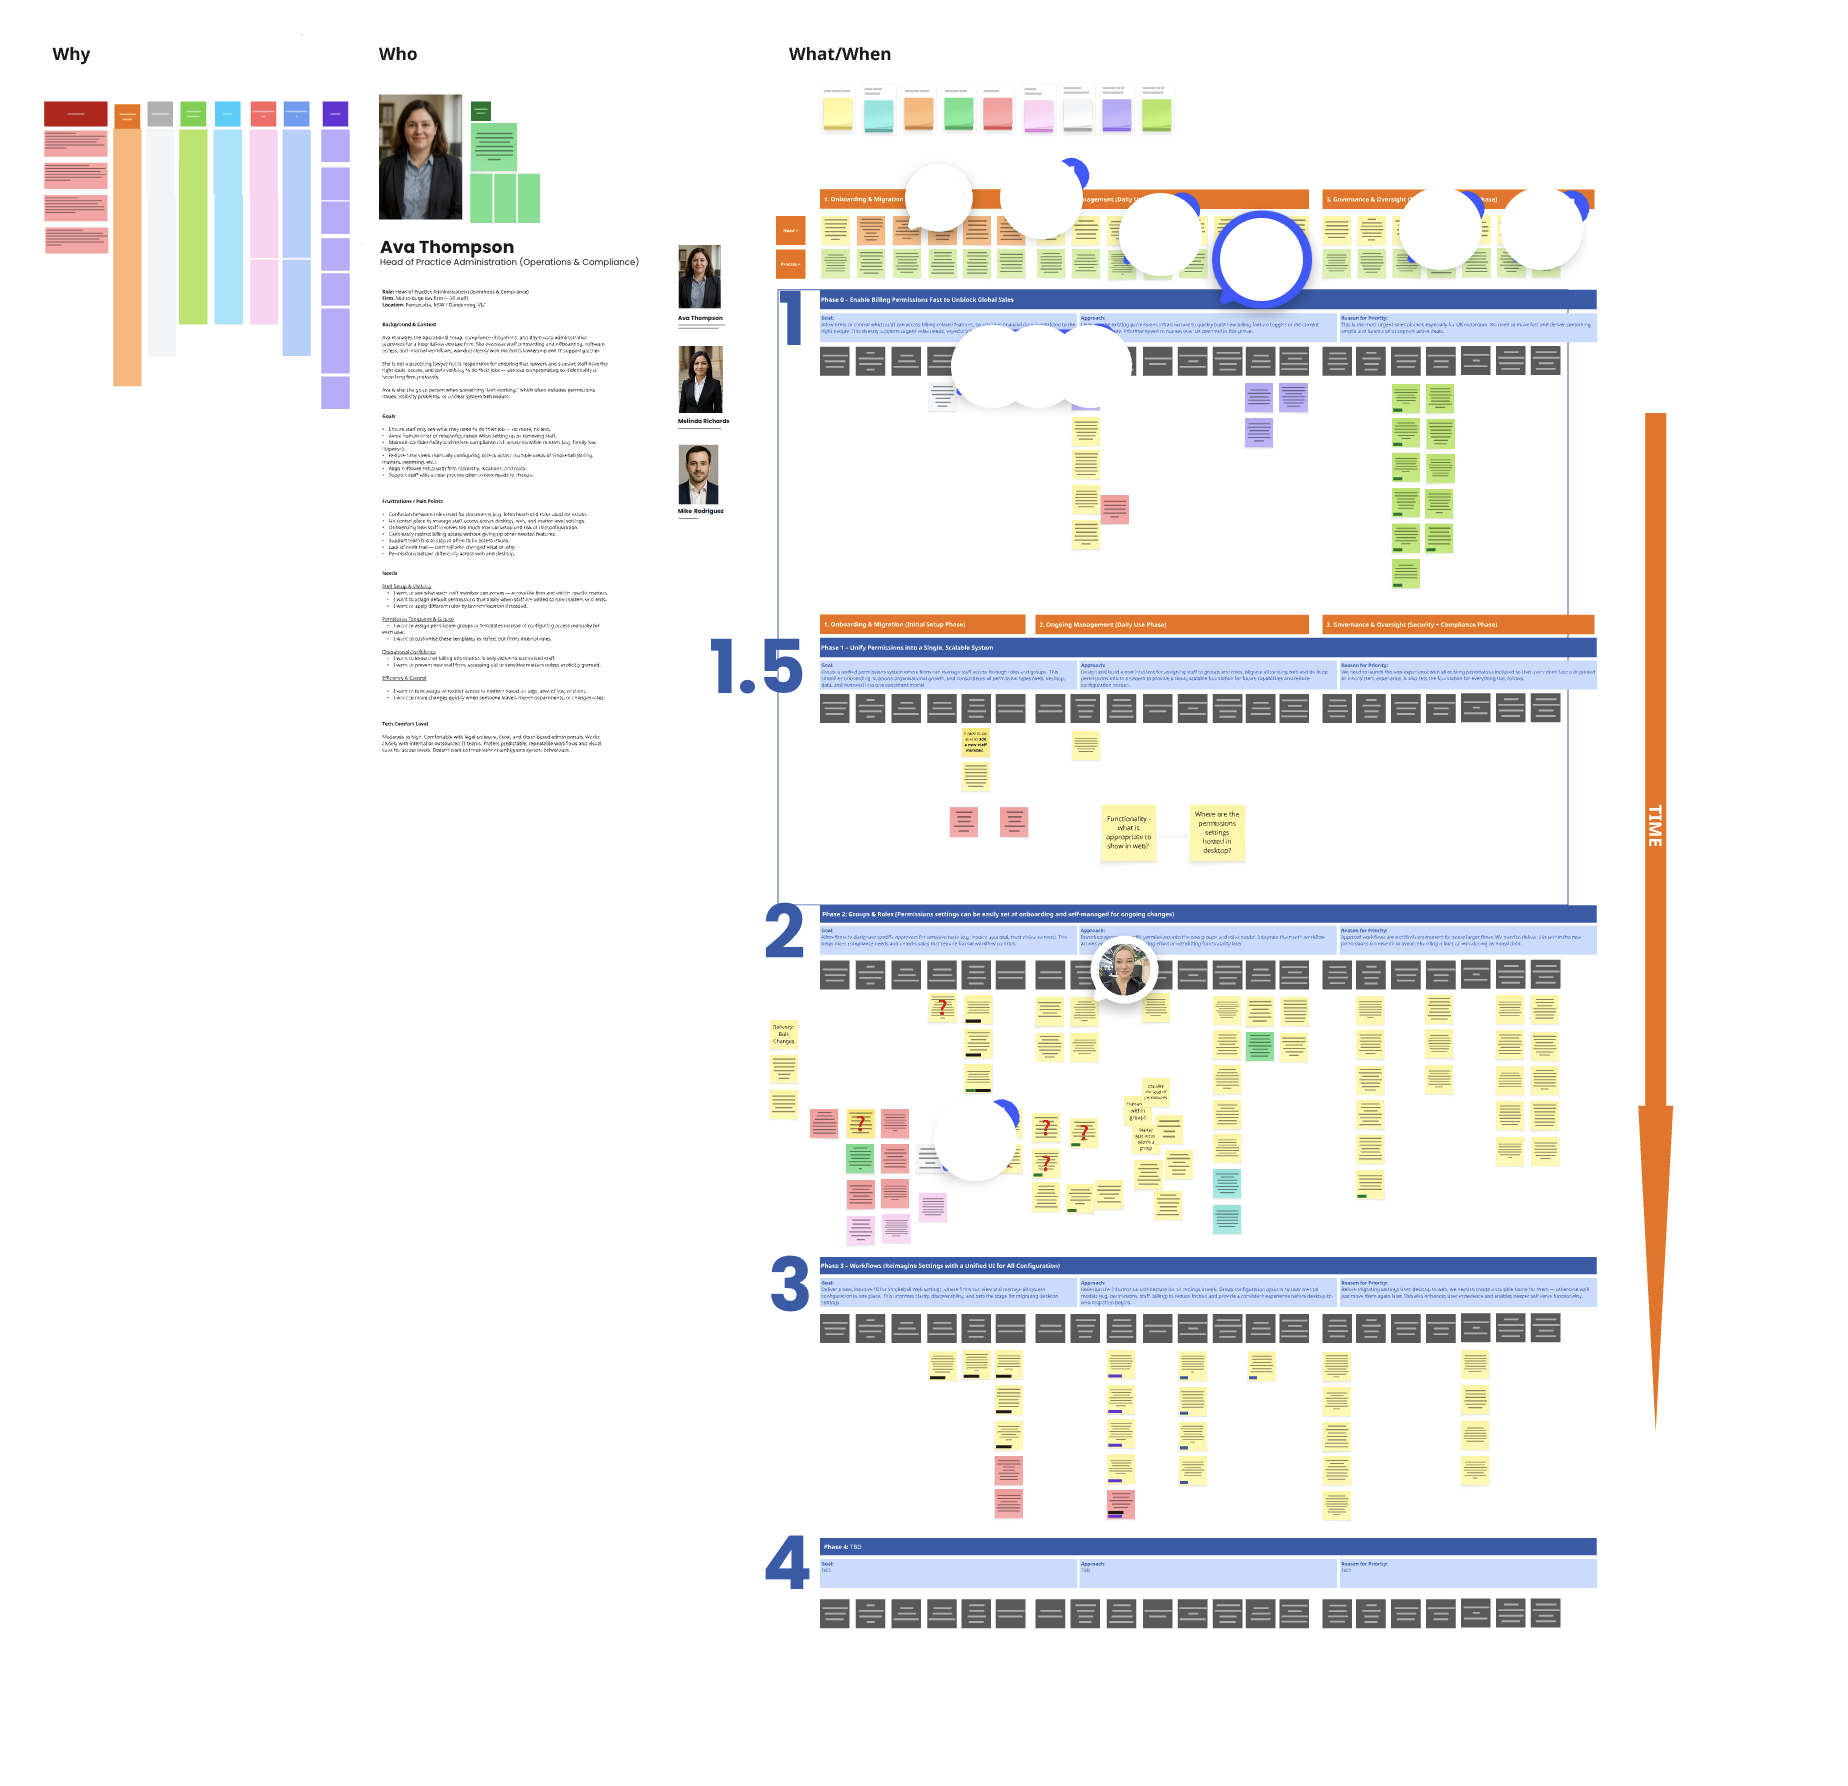
Designing role-based structures
Rather than assigning permissions individually to users, I explored group-based models where roles could define access levels for multiple users at once.
This approach reduces administrative overhead and improves consistency across firms.
Balancing flexibility and usability
Permission systems can quickly become overwhelming for administrators. I focused on designing patterns that would allow firms to configure permissions without creating unnecessary complexity.
Outcome
The work helped establish a foundation for more scalable permission management within the platform.
Key outcomes included:
clearer models for role-based access control
improved scalability for larger firms
reduced administrative complexity when managing permissions.
What This Demonstrates
This project highlights my experience designing complex systems within enterprise products, where usability, security, and scalability must all be carefully balanced.